Zero access. Your data stays yours.
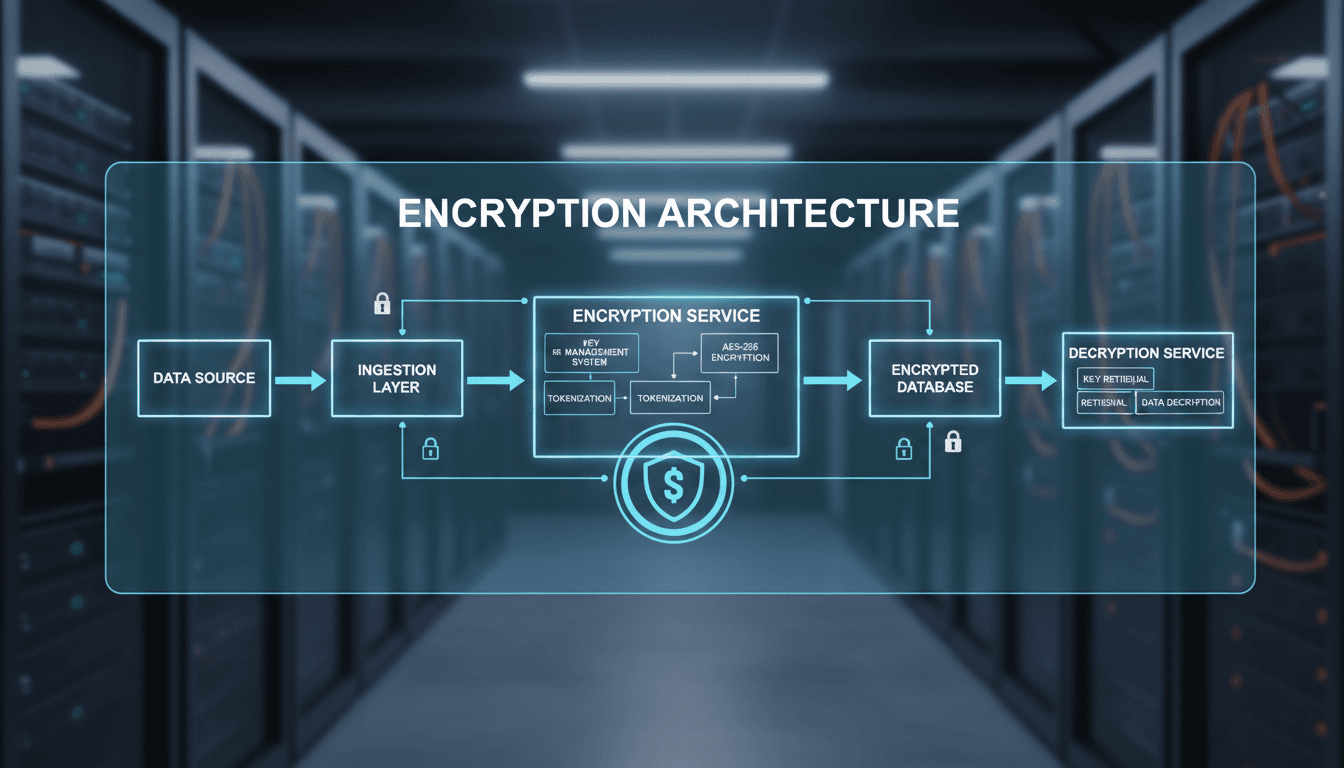
Fableapp is built on a security-by-design architecture. End-to-end encrypted by default, with architecture we're prepared to defend.
We can't read your messages. That's the point.
Fableapp's architecture is built on zero-access principles and minimal metadata, so your conversations stay private by design, not by promise.
Zero-access servers
Message content is encrypted before it leaves your device. Our servers store ciphertext, not your words.
Metadata-minimizing design
We collect the least data needed to deliver messages, then discard what we don't require.
Encrypted local storage
Messages remain encrypted at rest on your device, protected even when your phone is locked.
No plaintext, ever
From transit to storage, your data stays encrypted. There's no backdoor, and no way in for us.
Encryption and hardware questions
If you have further security questions, contact us.
Encrypted storage, locked on your device
Fableapp keeps messages and files encrypted at rest with SQLCipher, then locks everything behind your device's own biometrics. Your data stays local, protected, and private.
100%
Encrypted at rest
SQLCipher encrypts every locally stored message and file before it touches the disk.
AES-256
Database encryption
Your local database is protected with bank-grade hardware-backed AES-256 encryption.
0
Cloud databases
We don't store your conversation database on any cloud server. It stays on your device.
BIOMETRIC
App lock default
Face ID or fingerprint unlock is the default gate before any message becomes visible.
Found a vulnerability? Tell us directly.
We treat every report seriously and respond quickly. Your findings help us keep Fableapp secure for everyone.